Centralized rule management
Review and maintain rules in one place to reduce inconsistent changes between devices.
Every permitted connection should have a reason.
Hisn Firewall focuses on the source, destination and business purpose behind a network rule. Exceptions are easier to manage when they have an owner and a review point. Discuss the application's required traffic, change approvals and the evidence the operating team needs to investigate a blocked or unexpected connection.
Firewall rules become hard to review when their purpose and owner are missing.
Explore how the product could bring its tools and working records into one view. Review the workflow design during your product walkthrough.
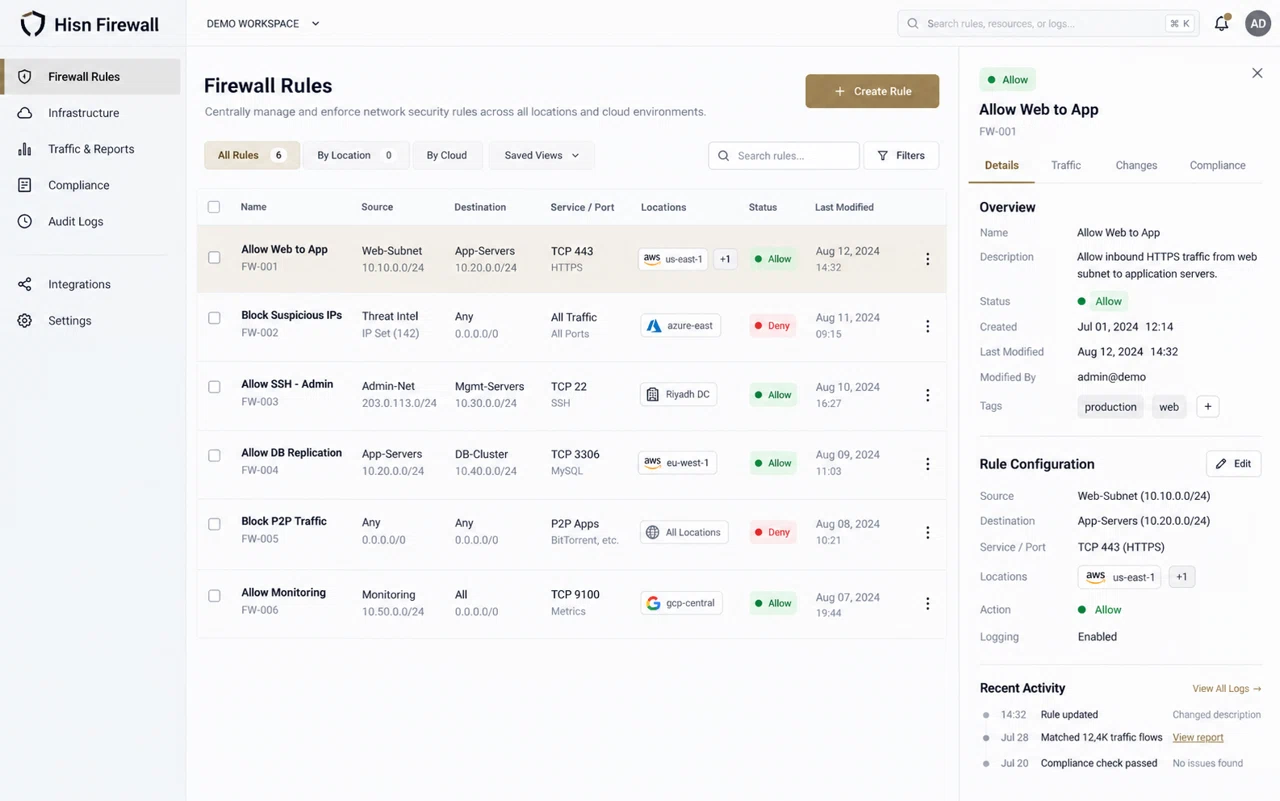
Connect each capability to a day-to-day task and a practical result your team can evaluate.
Review and maintain rules in one place to reduce inconsistent changes between devices.
Compare protection settings across supported sites and cloud environments.
Trace who changed a rule and when so incidents and reviews have a usable history.
Bring one example from your daily work. We can review the records involved, who owns each step and which integrations are needed before defining the implementation scope.
Discuss your workflowA management workspace organizes policies, change records and visibility, helping teams understand the access each rule allows.
Review the rule allowing one business application, including its source, destination and owner. Remove an expired exception in a controlled test. Maintain enough context to explain why each permitted connection exists.
An illustrative scenario to discuss when planning your project.The people involved include network engineers, security reviewers and change owners. Begin with a small, representative set of network zones, existing rules, application dependencies and change approvals, then identify the decision or action each role needs to complete. This helps shape a useful first release and avoids collecting information that nobody uses.
Useful security operations link a signal or policy decision to evidence, an owner and a response process. Agree the authorized scope, review permissions and handling of exceptions. Include benign activity in evaluation as well as controlled test events, so the team can assess the practical review workload.
Identify the current sources of network zones, existing rules, application dependencies and change approvals. Check data quality, shared references and required fields before agreeing what will be migrated, connected or recreated.
Review the needs of network engineers, security reviewers and change owners. Document permissions, required integrations, the authoritative system for each record and what happens when information cannot be exchanged.
Use safe sample data to review a rule change, verify permitted traffic and trace the approval history. Agree expected results, review exceptions and record acceptance decisions before widening access.
Name the configuration owner, change decision-maker and support contact. Plan training and documentation around ordinary tasks, then review early use under the agreed support arrangement.
Prepare examples of network zones, existing rules, application dependencies and change approvals, with confidential details removed. Explain the step that takes the most effort or causes confusion, and identify who needs to review the result.
We define a scenario that lets your team review a rule change, verify permitted traffic and trace the approval history. Compare the result with the current process and document requirements and gaps before approving the implementation scope.
The required systems and data sources are reviewed first. The integration plan covers access, field mapping, transfer timing and responsibility for errors. The proposal identifies included connections and any custom work needed.
The proposal considers features, users or workload, the operating environment, integrations and migration. Training, operational ownership and the support arrangement are agreed alongside the implementation scope.