Authentication & rate limiting
Check credentials and apply request limits at the entry point to manage who can call an API and how often.
A clear front door for application requests.
Bawwaba API focuses on the rules at the entry point between a caller and a service. Authentication, permitted routes and request limits need understandable responses. Review ordinary traffic, rejected access and retries with the consuming team so the gateway is part of a dependable application journey.
A gateway provides a controlled entry point for API traffic.
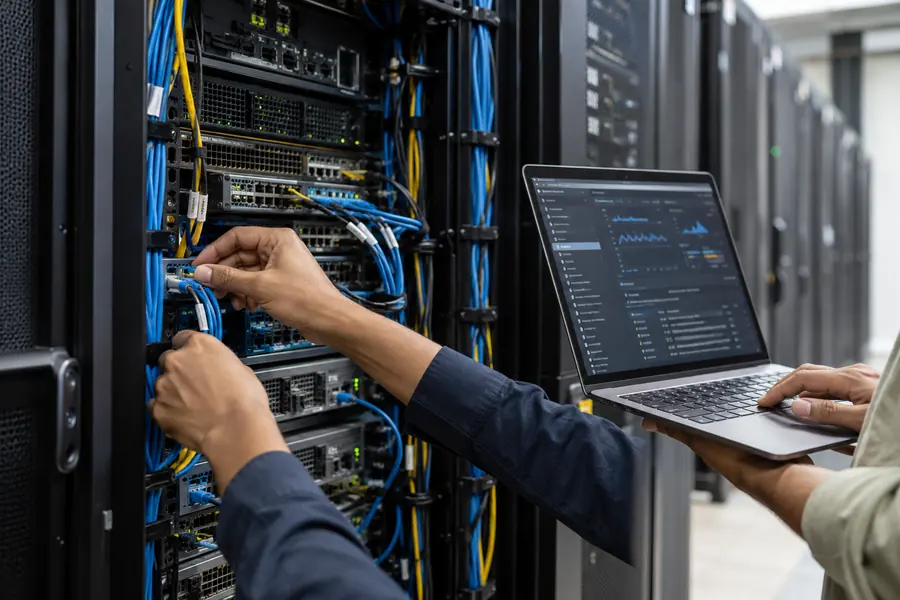
Explore how the product could bring its tools and working records into one view. Review the workflow design during your product walkthrough.
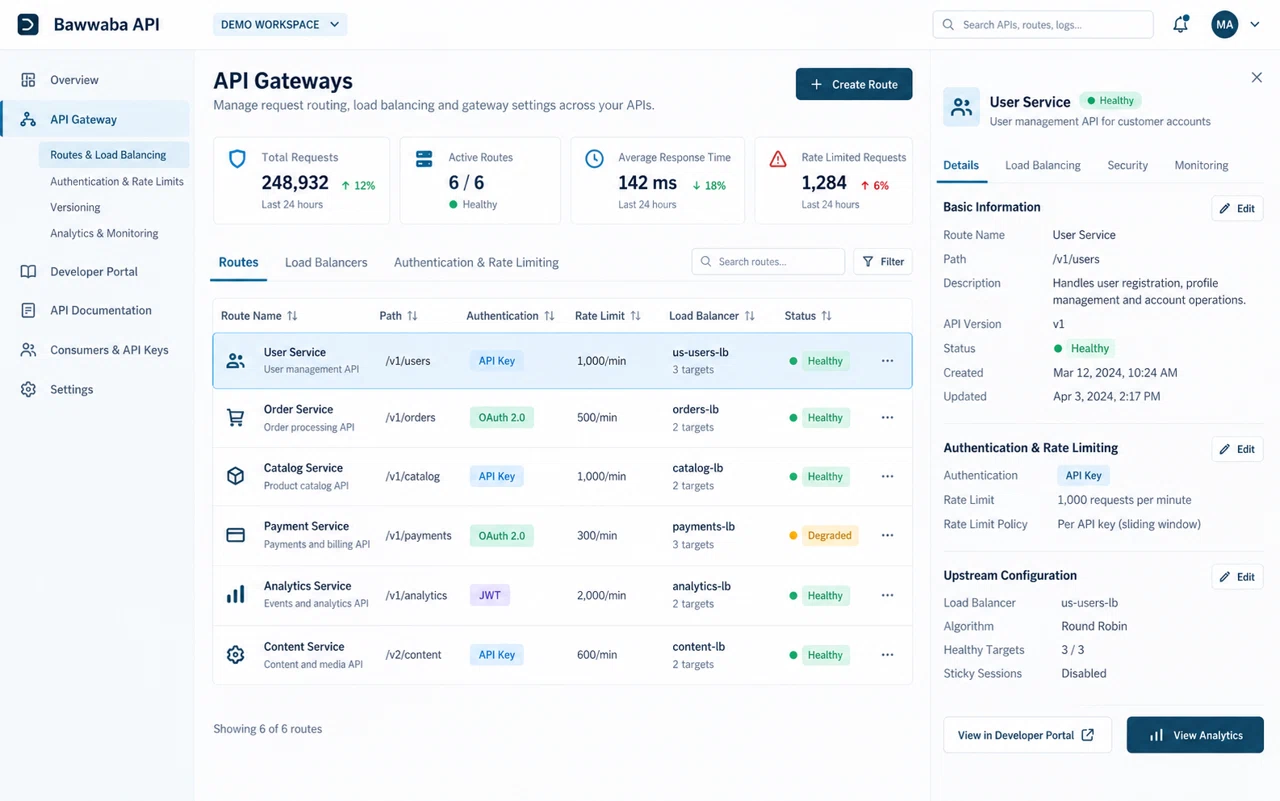
Connect each capability to a day-to-day task and a practical result your team can evaluate.
Check credentials and apply request limits at the entry point to manage who can call an API and how often.
Route requests to the intended backend so clients use a consistent entry point.
Inspect request volume and errors to locate service issues that affect integrations.
Bring one example from your daily work. We can review the records involved, who owns each step and which integrations are needed before defining the implementation scope.
Discuss your workflowIts configuration needs to match authentication, routing and rate policies without hiding useful errors from developers. Operational visibility helps teams distinguish a gateway issue from an application issue.
Call a protected route with valid access, expired credentials and too many requests. Review what the client sees in each case and where the event is logged. Rules should be explicit enough for the consuming team to troubleshoot.
An illustrative scenario to discuss when planning your project.The people involved include API developers, platform operators and security reviewers. Begin with a small, representative set of route definitions, authentication requirements, traffic profiles and upstream services, then identify the decision or action each role needs to complete. This helps shape a useful first release and avoids collecting information that nobody uses.
A working setup needs more than a successful first deployment. Agree access, environment boundaries, monitoring, recovery and change ownership. Review a normal operation and an interrupted one before handover, with clear instructions for diagnosing the issue and deciding whether to retry, restore or roll back.
Identify the current sources of route definitions, authentication requirements, traffic profiles and upstream services. Check data quality, shared references and required fields before agreeing what will be migrated, connected or recreated.
Review the needs of API developers, platform operators and security reviewers. Document permissions, required integrations, the authoritative system for each record and what happens when information cannot be exchanged.
Use safe sample data to route a valid request and reject an unauthorized or rate-limited request with a traceable result. Agree expected results, review exceptions and record acceptance decisions before widening access.
Name the configuration owner, change decision-maker and support contact. Plan training and documentation around ordinary tasks, then review early use under the agreed support arrangement.
Prepare examples of route definitions, authentication requirements, traffic profiles and upstream services, with confidential details removed. Explain the step that takes the most effort or causes confusion, and identify who needs to review the result.
We define a scenario that lets your team route a valid request and reject an unauthorized or rate-limited request with a traceable result. Compare the result with the current process and document requirements and gaps before approving the implementation scope.
The required systems and data sources are reviewed first. The integration plan covers access, field mapping, transfer timing and responsibility for errors. The proposal identifies included connections and any custom work needed.
The proposal considers features, users or workload, the operating environment, integrations and migration. Training, operational ownership and the support arrangement are agreed alongside the implementation scope.